20+ years ago, I graduated from Addis Ababa University and began a journey that started deeply in technology.
I was fortunate to grow through the technical trenches—not just managing technology, but building, operating, troubleshooting, securing, and leading technology platforms.
My early career was shaped by intensive technical exposure and certifications, moving from MCSA to MCSE on the Microsoft Windows platform, starting with the Windows NT era, and progressing from CCNA toward CCIE on Cisco platforms, as well as from RHCA toward RHCE on Red Hat platforms.
For years, I was a technical guru, engineer, architect, and technical leader.
I lived technology.
I worked with infrastructure, networks, operating systems, enterprise platforms, security, projects, and technical teams. This experience gave me something that I consider invaluable today: the ability to understand technology from the inside out.
But somewhere along that journey, I discovered something profound:
The biggest gap in digital transformation is not always a technical gap.
Organizations can have talented engineers, sophisticated technologies, powerful infrastructure, and modern applications—and still struggle to realize sustainable value.
The deeper gaps are often found in:
Governance.
Risk.
Compliance.
Accountability.
Processes.
Standards.
Assurance.
And the adoption of proven best practices.
That realization became a turning point in my career.
From Technical Guru → Digital GRC Practitioner
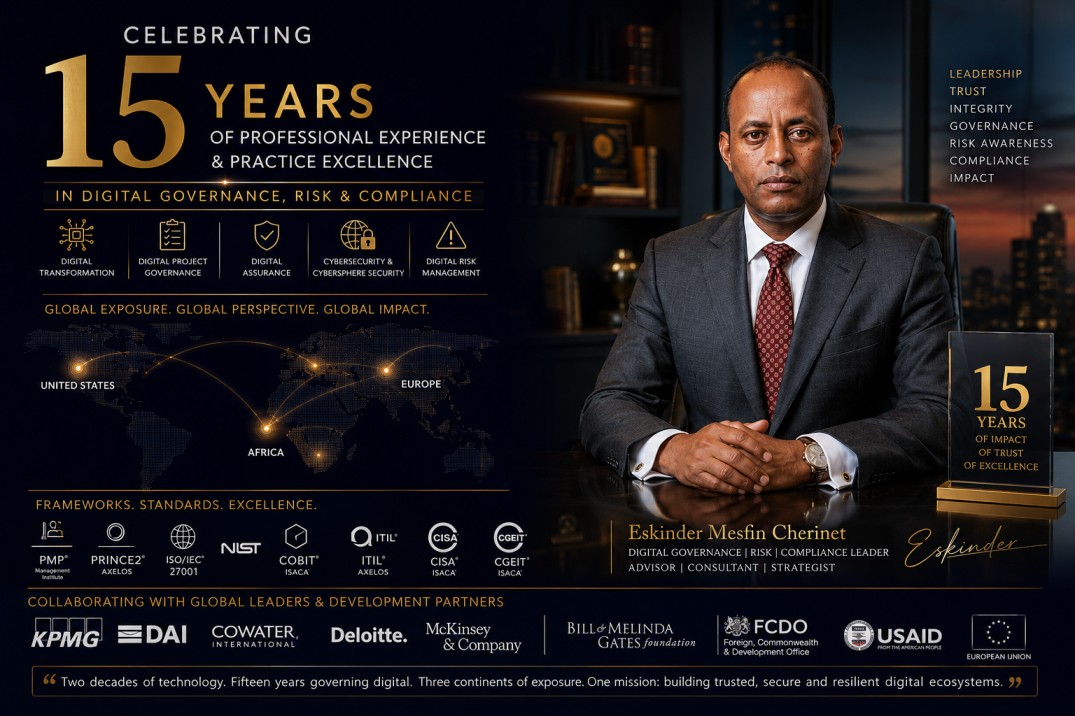
Around 15 years ago, I began my transition into Digital Governance, Risk & Compliance (GRC).
And I owe a special appreciation to Kenya, which played an important role in opening my eyes to the broader world of GRC and exposing me to a different dimension of professional practice.
Since then, my journey has expanded from technology implementation to governing technology, assuring digital investments, managing digital risks, strengthening cybersecurity, and helping organizations transform responsibly.
Over these 15 years, I have had the privilege of gaining professional exposure across Africa, Europe, and the United States, working with global consulting firms, international organizations, development partners, and complex digital transformation programs.
My journey has included practical exposure to:
🔹 Digital Transformation & Strategy
🔹 Digital Project Governance
🔹 Digital Assurance & Audit
🔹 Cybersecurity & Cyber Resilience
🔹 Digital Risk Management
🔹 IT Governance & Compliance
🔹 Enterprise Architecture
🔹 IT Service Management
🔹 Digital Trust & Resilience
Along the way, globally recognized frameworks, standards, and professional practices have become part of my daily vocabulary:
PMP | PRINCE2 | COBIT | ITIL | ISO/IEC 27001 | NIST | CISA | CGEIT
I have also been privileged to work with or gain exposure through leading global consulting and development organizations, including KPMG, DAI, Cowater, Deloitte, and McKinsey, alongside development partners such as BMGF, FCDO, USAID, and the European Union.
Looking Back
When I reflect on the journey, I see two very important chapters:
20+ years of technology and professional practice.
15 years of Digital GRC.
The first taught me how technology works.
The second taught me how technology should be governed, secured, assured, managed, and aligned with organizational objectives.
And perhaps the most important lesson has been this:
You cannot govern what you do not understand.
My technical foundation continues to shape the way I approach GRC today. I believe effective Digital GRC professionals need to understand both sides of the equation—the technology and the governance surrounding it.
I am deeply grateful to Addis Ababa University, Kenya, colleagues, mentors, clients, global consulting firms, development partners, and every professional community that has contributed to this journey.
20+ years since graduation.
15 years in Digital GRC.
Three continents of professional exposure.
One continuing mission: Building trusted, secure, resilient and well-governed digital ecosystems.
The journey continues.
Eskinder Mesfin Cherinet
Digital Governance | Risk | Compliance | Cybersecurity | Digital Transformation
#20Years #15YearsGRC #DigitalGRC #DigitalGovernance #DigitalTransformation #Cybersecurity #DigitalRisk #DigitalAssurance #ITGovernance #COBIT #ITIL #NIST #ISO27001 #CISA #CGEIT #PMP #PRINCE2 #DigitalTrust #Africa #Europe #USA #ProfessionalJourney
No responses yet